Cybercriminal Extraditions From Third Countries to the US
How US prosecutors use infrastructure connections and treaties to extradite foreign cybercriminals.
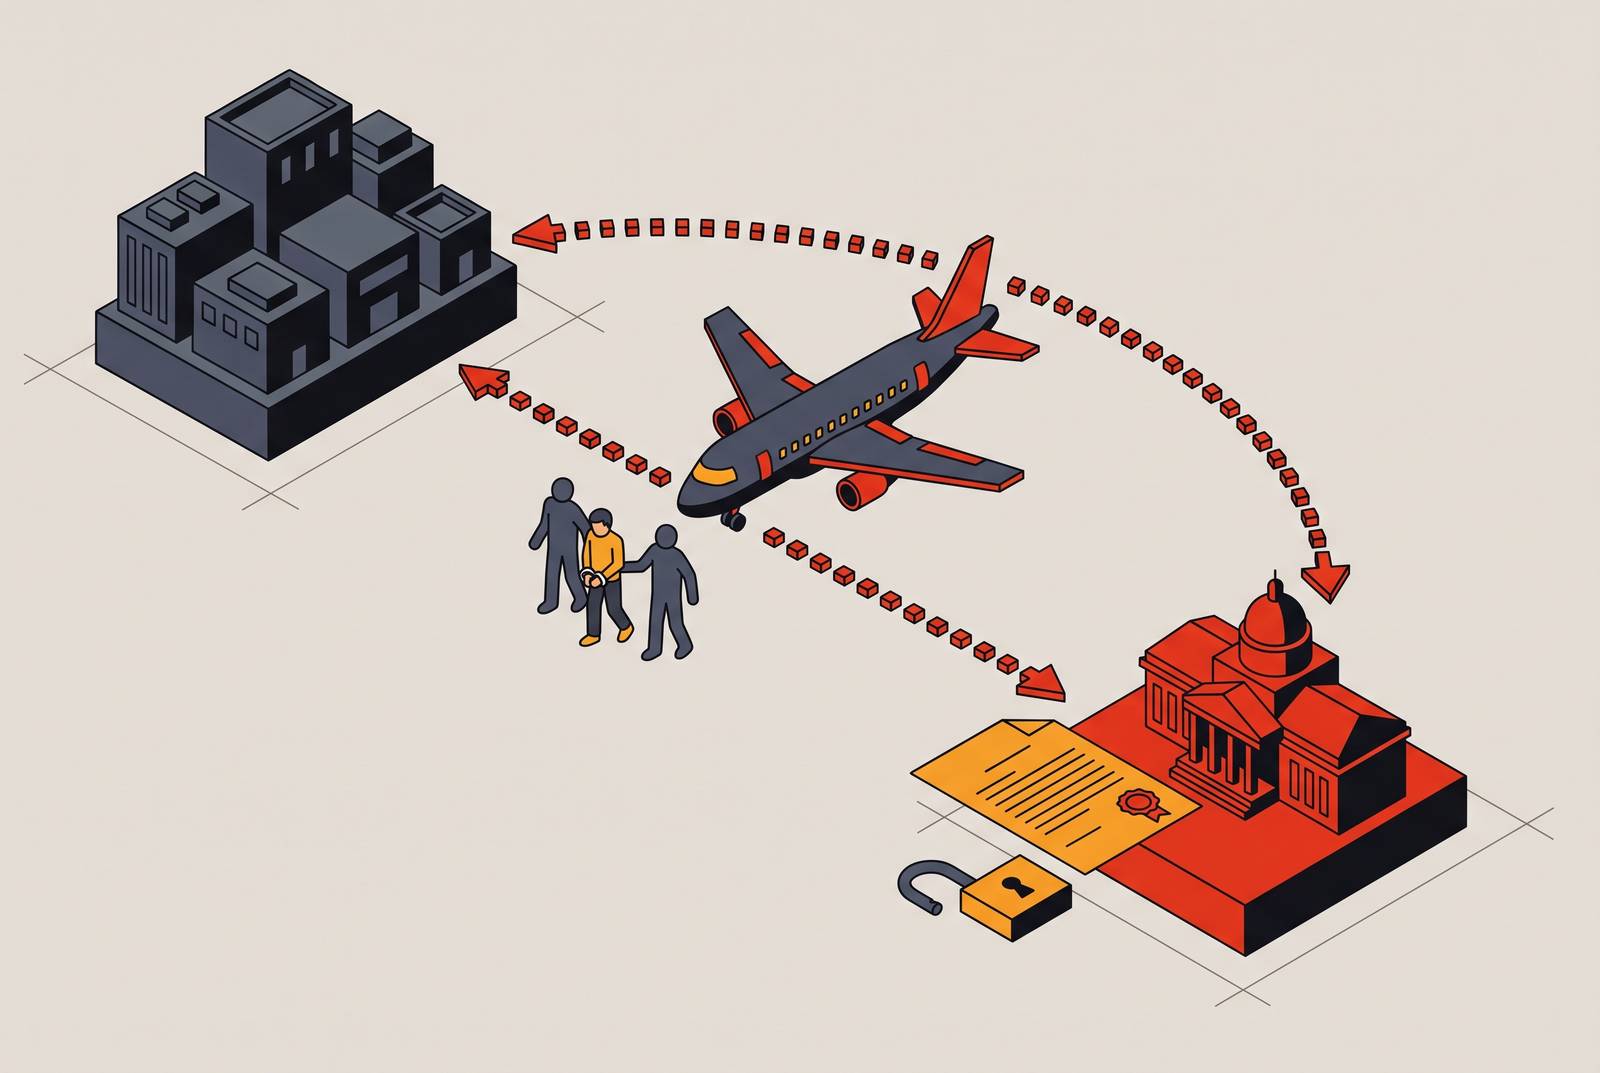
Cybercriminal extraditions from third countries to the US follow a specific, repeatable playbook: long-arm jurisdiction, Interpol Red Notices, provisional arrest requests, and a treaty network that is far more flexible than most people assume.
How the US asserts legal authority over cybercriminals outside its borders
US criminal jurisdiction does not require a US passport, a US zip code, or a single day spent on US soil. It requires a connection, and the bar for "connection" is low. If a transaction touches a US server, a US payment processor, or US financial infrastructure, federal prosecutors treat that as enough of a foothold to charge someone who has never set foot on US soil.
The UK-US relationship shows this in plain terms. Picture a merchant running a Shopify store out of Bristol. A customer in Florida pays through Stripe, the bank later calls the charge fraudulent, and Stripe's US arm flags the transaction to federal regulators. From there it is a short walk to a wire fraud charge, built entirely on the fact that the money passed through US-connected infrastructure. The merchant's location never factored into it.
Three charges do most of the heavy lifting in cases like this: wire fraud, money laundering, and computer fraud. All three attach whenever US infrastructure sits anywhere in the chain, whether that is a bank, a payment processor, or a server rack somewhere in the US. Even something as mundane as a .com domain name counts, since Verisign, the registry that runs .com, is a US company. Once that link exists, a defendant's IP address or home address stops mattering legally. The case can move forward no matter which country the person is actually in.
That's the doctrine in a sentence: touch US infrastructure, and you've handed US prosecutors a reason to come looking. What happens next is where the real work begins.
The Third-Country Arrest Mechanism
Federal prosecutors indict foreign suspects they have no way of physically reaching all the time. An indictment against someone living comfortably in a country with no meaningful cooperation with Washington does nothing on its own. It just sits there, a piece of paper with teeth it can't use yet. The indictment is the opening move, not the finish line. Its real job is to set off a chain of international enforcement steps that may or may not land.
The sequence runs like this. The Department of Justice indicts the suspect and gets an arrest warrant. The DOJ's Office of International Affairs sends a provisional arrest request through diplomatic channels to whichever country the suspect might be in or passing through. Interpol issues a Red Notice, broadcast to law enforcement in all 196 member countries, asking them to locate and provisionally arrest the person. A Red Notice is a request, not an order. Every country decides for itself, under its own laws, whether to act on it.
A missing extradition treaty sounds like it should be a dealbreaker, and it isn't. Extradition law specialists point out that deportation, immigration removal, reciprocity-based cooperation, and plain Interpol-driven police action can all step in where no formal treaty exists. Countries have more than one lever to pull, treaty or no treaty.
Timing is where this gets tight. Once a suspect is spotted in a country willing to cooperate, the provisional arrest request has to move fast, because the window between "we found him" and "he's on a flight somewhere else" can be short. If the arrest holds, a formal extradition package follows, built to satisfy the receiving country's own legal standard, including a requirement known as dual criminality: the conduct has to be a crime in both countries, not just the one asking for the suspect.
The March 2025 Coordinated Extraditions
None of this runs as a series of one-off favors between governments. The clearest proof came in March 2025, when the Justice Department returned more than a dozen fugitives from ten different countries in a single month. Colombia, the Dominican Republic, France, Guatemala, Honduras, Israel, the Kyrgyz Republic, Mexico, Spain, and the United Kingdom all cooperated inside the same window, handing over defendants facing everything from cybercrime and fraud to murder and drug trafficking. That's not luck; it's a standing pipeline that multiple governments plug into at once.
Among the cybercrime defendants returned that month was Bikramjit Ahluwalia, 39, a dual citizen of the United Kingdom and the UAE, extradited from Spain on charges of conspiracy to commit wire fraud, money laundering conspiracy, conspiracy to damage a protected computer, and wire fraud, tied to an alleged tech support fraud scheme. Spain, a reliable US extradition partner, processed the case without the friction that appears in less aligned countries.
The same cycle produced a genuine first: the extradition of Danhong "Jean" Chen, 60, an immigration attorney facing visa fraud charges, from the Kyrgyz Republic. The DOJ flagged it as the first extradition ever completed from the Kyrgyz Republic to the US on federal criminal charges. One data point doesn't prove a trend, but it does show the network of cooperating states creeping into territory it hadn't reached before.
How individual high-profile cybercriminal cases expose the process
Looking at the mechanics in the abstract only gets you so far. The individual cases are where each gear of the machine becomes visible, and lined up in order, they trace a path from best-case scenario to hard limit.
Start with the Red Notice doing its job well. Amir Barati, an Iranian man accused of taking part in a hacking campaign tied to the Mabna Institute (a group blamed for looting data from universities and companies), was arrested in Montenegro in June at the FBI's request. He was extradited on October 1, 2026, to face wire fraud and computer fraud charges in the Southern District of New York. Montenegro is deeply wired into Western law enforcement cooperation, and the country acted on the FBI's request within days or weeks of locating him. The whole extradition wrapped in roughly three months, which is fast by the standards of this kind of case.
Move to a fast bilateral relationship working exactly as designed: the Kosovo extraditions of Ardit Kutleshi, 26, and Jetmir Kutleshi, 28, alleged administrators of the Rydox cybercrime marketplace. Both were extradited from Kosovo in April 2025 to face identity theft, access device fraud, and money laundering charges in the Western District of Pennsylvania, and Ardit later pleaded guilty. Kosovo is a small country, but its alignment with Western law enforcement makes it a dependable partner, even for marketplace-level cybercrime that doesn't carry the same political weight as state-backed hacking.
Then there's a case that shows deliberate caution built into the system. Victoria Dubranova, 33 (also known online as Vika, Tory, and SovaSonya), a Ukrainian national, was indicted for cyberattacks on critical infrastructure carried out in support of Russian geopolitical interests as part of a group called CyberArmyofRussia_Reborn. The case grew out of Operation Red Circus, an ongoing FBI effort against Russian state-linked cyber threats. Her country of arrest was never disclosed, which looks less like an oversight and more like operational security in a case with real political sensitivity attached.
Add Tyler Buchanan, 23, a UK national extradited from Spain in the same window of cases to face conspiracy to commit computer intrusion, wire fraud, and aggravated identity theft in the Central District of California, tied to phishing attacks on dozens of companies and the theft of millions in cryptocurrency. He's one more Scattered Spider-linked defendant moved through the same Spain-to-US channel that handled Ahluwalia, confirming this route as a routine pipeline.
Finally, the case that shows where the system hits its ceiling. Xu Zewei, a Chinese national accused of taking part in state-sponsored hacking tied to the group known as Silk Typhoon, was extradited from Italy on April 25, 2026, after the FBI requested his arrest with help from the Cyber Division of the Italian National Police. It's a rare event: a Chinese hacker actually standing before a US court. The DOJ has indicted plenty of Chinese hackers living abroad, but has only managed to convict one Chinese intelligence officer extradited on espionage and trade secret charges. Xu Zewei reached a courtroom because he happened to be in Italy, a country that cooperates with the US. China's government never had to make a choice.
Treaty Gaps, State Sponsorship, and Safe-Haven States
Every mechanism described so far depends on one condition: the suspect has to leave the country that shelters them. That's the ceiling the whole system runs into. A cybercriminal who is a citizen of, or protected by, Russia, China, Iran, or North Korea, and who stays inside that country, is functionally out of reach no matter how many Red Notices get filed.
The US has no extradition treaty with Russia or China, the two countries most frequently named as sources of significant cyber threats. It's a structural gap, and no amount of coordination between the DOJ, Interpol, and the Office of International Affairs closes it as long as the shelter country refuses to hand anyone over.
State sponsorship makes the problem worse than an ordinary treaty gap. A shelter state has never handed over military officials indicted in the US for hacking, and Xu Zewei's case worked only because he happened to be standing in another country when the request went out, not because the shelter state decided to cooperate. The same logic explains Barati: his case is a genuine success story, one of the rare instances where someone accused of working with an Iranian state-backed hacking operation actually reaches an American courtroom, and it happened because he was traveling through Montenegro while staying home in Iran would have kept him out of reach.
Countries without a formal treaty can still choose to cooperate. The Maldives, which has no extradition treaty with the US, handed over Roman Seleznev anyway. But that kind of cooperation is a choice a government makes in the moment, shaped by its own politics and relationships, not a guarantee built into any legal framework. A missing treaty changes which route a case has to take to reach the US. For state-sponsored hackers, though, the political route is closed too, since the government sheltering them is the same government that sponsored the operation.
What extradition deters, versus merely constrains geographically
Whether any of this actually stops people from hacking in the first place is a fair question, and the honest answer is mixed. Threatening prison time tells the world that a government takes these crimes seriously, which has its own value. But a deterrent only works if the target believes it will actually be used, and extradition's success rate, especially against state-backed actors, undercuts that belief. One former US intelligence and law enforcement official put it bluntly: extradition is "more of a political tool than a useful deterrent."
The IntelBroker case makes the limits concrete. After the alleged operator behind the IntelBroker persona was arrested in February 2025, the persona itself went quiet. But the data stolen under that name kept circulating, and other brokers picked up the slack selling similar material. Arresting one person didn't shut down the market. It just created a vacancy that got filled fast.
What extradition does reliably accomplish is narrower and more useful: it raises the cost of operating. Indictments and extraditions, even the ones that never fully land, force threat actors to operate under constant counterintelligence pressure. They shrink the list of countries a hacker can safely travel through. And they send a clear signal to the mid-tier associates around any major operation that an operational security slip can turn into a personal legal problem, prison included. Call it capability degradation. It's a smaller claim than "this stops hacking," but it's the one the evidence actually supports.
Threat intelligence produced by unsealed indictments and extradition cases
Federal indictments, once unsealed, hand defenders something most commercial threat reports can't match: government-certified detail. They name specific infrastructure, lay out tactics and techniques with precision, and carry the evidentiary weight of a case the government is prepared to argue in court.
The IntelBroker case shows what that detail looks like in practice. Authorities traced a Bitcoin payment to a Ramp exchange account linked to the suspect, with a separate Coinbase account providing further corroboration. Those are the same kinds of digital artifacts, cryptocurrency transaction records, reused email addresses, forum account activity, API key sales to undercover agents, that internal security teams can hunt for in their own logs and telemetry. The government is using the same trail defenders already have access to.
A gap opens after an arrest happens that's worth watching closely. Successor actors move in fast, stolen data keeps circulating under the original persona's name, and a security team that treats an arrest as the end of a threat will miss the window where old breach data quietly re-enters the market under new management.
The Scattered Spider cases give defenders a concrete example of what this intelligence looks like when it's usable. Peter Stokes, extradited in 2026, and Tyler Buchanan, extradited in 2025 and later pleading guilty, both come with named infrastructure, documented phishing methods used against dozens of companies, and ransom payment chains laid out in detail. That's a working map for any security team in the sectors those two targeted.
DOJ press releases and unsealed indictments function as a standing feed of government-sourced tactics and techniques, free to read and sitting in plain view. Most security teams never open them.